Multi vendor, and the matrix says where the gaps are
What follows is not the list of what NacTrack can learn to read, it is the list of what it already reads, empty cells included. A platform that is missing gets handled, not refused.
The vendors NacTrack reads
Each one is a row of the table below, with what is actually read from it, column by column and empty cells included.
- Cisco
- Huawei
- Juniper
- Aruba
- Arista
- Nokia
- Dell
- Fortinet
- F5
- Palo Alto Networks
- Infoblox
- Forcepoint





What is collected per platform
Coverage is published as it is, including the gaps.
CoveredPartialNot covered
| Platform | Inventory | Topology | Compliance | CVE | Spanning tree | MPLS and L2VPN |
|---|---|---|---|---|---|---|
| Cisco IOS 12 and 15 | Covered | Covered | Covered | Covered | Covered | Covered |
| Cisco IOS XE 16 and 17 | Covered | Covered | Covered | Covered | Covered | Covered |
| Cisco ASA | Covered | Partial | Covered | Covered | Not covered | Not covered |
| Cisco NX-OS | Covered | Covered | Covered | Covered | Covered | Partial |
| Cisco IOS XR | Covered | Covered | Covered | Covered | Not covered | Covered |
| Huawei VRP | Covered | Covered | Covered | Covered | Covered | Covered |
| Juniper Junos | by import | by import | by import | by import | Not covered | Not covered |
| Aruba AOS-CX | Covered | Covered | Covered | Covered | Not covered | Not covered |
| Aruba AOS | Covered | Covered | Covered | Covered | Not covered | Not covered |
| Dell OS10 | Covered | Covered | Covered | Covered | Not covered | Not covered |
| Arista EOS | by import | by import | by import | by import | Not covered | Not covered |
| Nokia SR OS | by import | by import | by import | by import | Not covered | Not covered |
| Fortinet FortiOS | Covered | Partial | Covered | Covered | Not covered | Not covered |
| F5 TMOS | Covered | Partial | Covered | Covered | Not covered | Not covered |
| Palo Alto PAN-OS | Covered | Partial | Covered | Covered | Not covered | Not covered |
| Infoblox NIOS | Covered | Not covered | Covered | Partial | Not covered | Not covered |
| Forcepoint NGFW | Covered | Partial | Not covered | Covered | Not covered | Not covered |
Compliance rule sets ship per platform, and most have a reference configuration set that tests them on every build. Forcepoint NGFW is collected but has no rule set yet: we would rather say so than evaluate it against another vendor's rules. Spanning tree is captured on Cisco and Huawei switches, MPLS and L2VPN on Cisco IOS, IOS XE, IOS XR and Huawei. Firewalls and load balancers appear in the topology through their addressing rather than a reported neighbour, since those platforms do not run LLDP or CDP. Juniper Junos, Arista EOS and Nokia SR OS are marked by import: you supply the configurations and command outputs, NacTrack parses them and shows them alongside the rest of the estate. Automatic SSH collection does not support these three platforms, and we would rather say so here than at deployment.
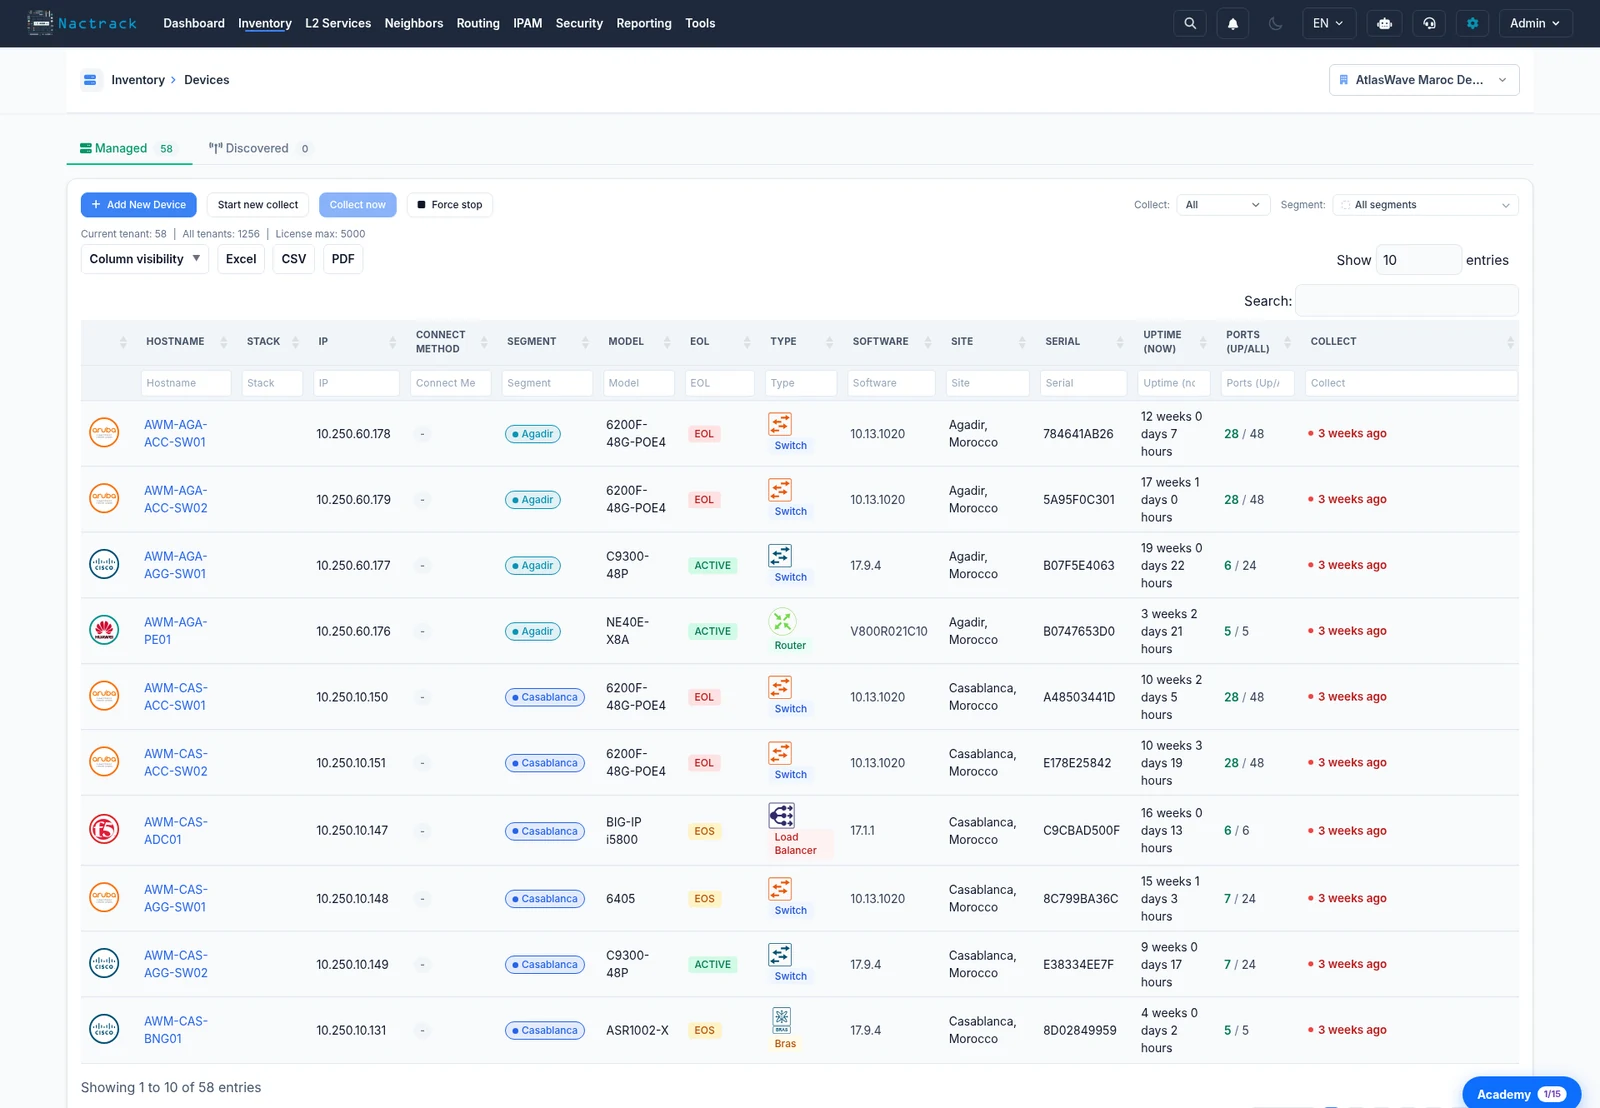
Two platforms read for something other than a switch
The columns above describe a network device. These two are collected to answer a different question, so they are described by what is read from them.
| Platform | What is read from it |
|---|---|
| Cisco ISE | Network access devices, live sessions with the 802.1X and MAB split, profiled endpoints, identity and endpoint groups, authorisation profiles, TrustSec with its SGTs, SGACLs and egress matrix, identity sources, TACACS profiles and command sets. |
| Cisco Catalyst 9800, on IOS XE | The controller, its access points, its WLANs, the radios and the associated clients. The controller is itself an IOS XE device, so the inventory, compliance and CVE of the IOS XE row already apply to it. |
Both of these surfaces are in the lab, and the product says so on screen on every one of their pages. The controller was validated against a real CW9800M; AireOS, the previous generation, is not supported and we would rather write that here.
What is asked of each platform, command by command
The table above says what you get. This says how. Open a platform to see the commands the collector sends it, grouped by what they bring back.
Cisco IOS and IOS XE45 SSH commands
Addressing
show ip dhcp bindingshow ip dhcp pool
Configuration
show running-config
Endpoints seen
show ip arpshow mac address-table
Inventory
show inventoryshow switch
Ports and interfaces
show interfacesshow interfaces transceiver detailshow ip interface briefshow ipv6 interface briefshow vlan briefshow vlans
Redundancy
show standby briefshow vrrp brief
Routing
show bfd neighborsshow bgp ipv4 unicast summaryshow bgp vpnv4 all summaryshow ip bgp ipv4 unicast summaryshow ip bgp vpnv4 all summaryshow ip eigrp neighborsshow ip ospf neighborshow ip route eigrpshow ip route isisshow ip route ospfshow isis database detailshow isis neighbors detail
Spanning tree
show spanning-treeshow spanning-tree detailshow spanning-tree mst detailshow spanning-tree vlan all detail
Topology
show cdp neighbors detailshow lldp neighbors detail
Transport and L2VPN
show bridge-domainshow ethernet service instance detailshow l2vpn service allshow l2vpn service vfi all detailshow l2vpn vfi detailshow mpls l2transport vcshow mpls ldp interfaceshow mpls ldp neighborshow mpls ldp neighbor detailshow vfishow xconnect allshow xconnect all detail
Cisco NX-OS24 SSH commands
Configuration
show running-config
Endpoints seen
show ip arpshow mac address-table
Inventory
show inventoryshow system resources
Licensing
show license usage
Ports and interfaces
show interfaceshow interface statusshow ip interface briefshow vlan
Redundancy
show hsrp briefshow vrrp brief
Routing
show bgp all summaryshow bgp ipv4 unicast summaryshow bgp vrf all ipv4 unicast summaryshow ip eigrp neighborsshow ip ospf neighborshow ip route eigrpshow ip route isisshow ip route ospf
Spanning tree
show spanning-tree detailshow spanning-tree vlan 1-4094 detail
Topology
show cdp neighbors detailshow lldp neighbors detail
Cisco IOS XR5 SSH commands
Access lists
show access-lists ipv4 usage pfilter location all
Device health
show memory summaryshow processes cpu
Licensing
show license summary
Ports and interfaces
show policy-map interface all
Cisco ASA15 SSH commands
Configuration
show running-config
Endpoints seen
show arpshow mac-address-table
Inventory
show inventory
Ports and interfaces
show interfaceshow interface ip briefshow ipv6 interface briefshow nameif
Redundancy
show failover
Routing
show bgp summaryshow eigrp neighborsshow ipv6 routeshow ospf neighborshow routeshow route ospf
Huawei VRP30 SSH commands
Addressing
display ip pool
Configuration
display current-configuration
Device health
display cpu-usagedisplay memory-usage
Endpoints seen
display access-user briefdisplay arpdisplay ipv6 neighborsdisplay mac-table
Inventory
display devicedisplay elabeldisplay version
Licensing
display licensedisplay license resource usage
Ports and interfaces
display interface briefdisplay ip interface briefdisplay ipv6 interface brief
Redundancy
display vrrp brief
Routing
display bfd session alldisplay bfd statisticsdisplay bgp ipv6 peerdisplay bgp peerdisplay bgp vpnv4 peerdisplay isis peer
Spanning tree
display stp briefdisplay stp instance alldisplay stp interface
Topology
display lldp neighbor
Transport and L2VPN
display mpls l2vcdisplay mpls ldp interfacedisplay mpls ldp peer
Aruba AOS-CX20 SSH commands
Configuration
show running-config
Endpoints seen
show arpshow mac-address-table
Inventory
show moduleshow system
Ports and interfaces
show interfaceshow interface briefshow lacp aggregatesshow lacp interfacesshow vlan
Routing
show bgp all-vrf all neighborsshow ip ospf interface all-vrfsshow ip ospf neighbors all-vrfsshow ip route all-vrfs
Topology
show cdp neighbor-infoshow lldp neighbor-infoshow lldp neighbor-info detail
Transport and L2VPN
show evpn evi detailshow interface vxlanshow interface vxlan vteps
Dell OS1015 SSH commands
Configuration
show running-configuration
Endpoints seen
show ip arpshow mac address-table
Inventory
show inventoryshow inventory media
Ports and interfaces
show interfaceshow interface statusshow ip interface brief
Routing
show ip route
Spanning tree
show spanning-tree detail
Topology
show lldp neighborsshow lldp neighbors detail
Transport and L2VPN
show ip bgp l2vpn evpn summaryshow nve remote-vtepshow virtual-network
Fortinet FortiOS17 SSH commands
Device health
get system performance status
Endpoints seen
get system arp
Inventory
get hardware nicget system status
Ports and interfaces
get system interface physical
Routing
get router info bgp summaryget router info ospf neighborget router info routing-table all
Topology
diagnose lldp neighbor-detaildiagnose lldp neighbor-detail port1diagnose lldp neighbor-summarydiagnose lldprx neighbor summaryget system lldp neighbors
VPN
diagnose vpn tunnel listget vpn ipsec tunnel detailsget vpn ipsec tunnel summaryget vpn ssl monitor
Forcepoint NGFW7 SSH commands
Device health
cat /proc/cpuinfo
Endpoints seen
cat /proc/net/arp
Inventory
/usr/sbin/sg-dmidata/usr/sbin/sg-name/usr/sbin/sg-version
Ports and interfaces
cat /proc/net/dev
Redundancy
/usr/sbin/sg-cluster status
F5 TMOS7 SSH commands
Inventory
list /sys global-settings hostname
Licensing
list /sys license
Ports and interfaces
list /net interface
Other
list /net selflist /net trunklist /sys file ssl-certlist /sys management-ip
Palo Alto PAN-OS6 configuration sections
Inventory
device and system
Policies
NAT rulessecurity policiessecurity zones
Ports and interfaces
interfaces
Routing
static routes
Cisco ISE15 API objects
Endpoints seen
endpointendpointgroupprofilerprofile
Inventory
mnt: Versionnetworkdevice
Live sessions
mnt: Session/ActiveList
Policies
activedirectoryauthorizationprofileegressmatrixcellidentitygroupinternalusersgaclsgttacacscommandsetstacacsprofile
Cisco Catalyst 9800, on IOS XE9 SSH commands
Device health
show application status ise
Wireless
show ap dot11 24ghz summaryshow ap dot11 5ghz summaryshow ap dot11 6ghz summaryshow ap imageshow ap summaryshow wireless client summaryshow wireless summaryshow wlan summary
Infoblox NIOS5 API objects
Addressing
record:arecord:cnamerecord:hostrecord:ptrzone_auth
Juniper Junos13 recognised on import
Configuration
configuration header: # JUNOSshow configuration
Inventory
hostname directive: host-name <name>;show chassisshow chassis hardwareshow version
Ports and interfaces
show interfaces
Routing
show bgpshow isisshow ospfshow route
Topology
show lldpshow lldp neighbors
Nokia SR OS2 recognised on import
Configuration
configuration header: # TiMOS
Inventory
hostname directive: system name <name>
235 entries in total, extracted from the collector itself on 2026-08-29, revision e61e75f2, rather than copied by hand. Not everything is read over SSH: Cisco ISE and Infoblox answer through their own API, and PAN-OS is read from the configuration the device exports. And a platform NacTrack never logs into is still recognised: you upload a session log or a configuration and it is parsed. Juniper is the clearest case, its commands are named one by one in the import detector. Each platform's label says which of the four applies. For the SSH platforms the list is what is specific to that platform: the branches sit on a shared base, so a short list means little that is specific, not little coverage, and Cisco IOS XR is the clearest case of that.
What happens when your platform is not in the table
- You open a ticket. That is all we ask of you: the platform enters the support flow like any other request, and we carry it from there.
- The rest is our work. The parsing runs on text from a real device, and that text is gathered while the ticket is handled. There is no vendor API to obtain, no partnership to sign and no third party release to wait for.
- A platform comes in through import first, which gives inventory, compliance and CVE immediately, then moves to SSH collection once the command set has settled.
- Specific architectures take the same route: an inherited addressing plan, a hand built VPLS, a naming convention peculiar to your house get described in a ticket, then correlated like everything else.
Is your hardware covered?
Send us the list of your platforms, the answer is precise and quick.