Know what is on your network, and what it is exposed to
Three questions come up in every security committee and every audit. NacTrack answers each one with a dated figure you can put on the table.
The three questions
- 1
What exactly do we own?
Models, software versions, sites. The usual answer is a file built during an old project. The question turns serious when an auditor asks to cross check it.
- 2
What are we exposed to?
Which devices a published vulnerability actually reaches, and which are no longer supported by their vendor. Two lists, and they decide a budget.
- 3
What can we state?
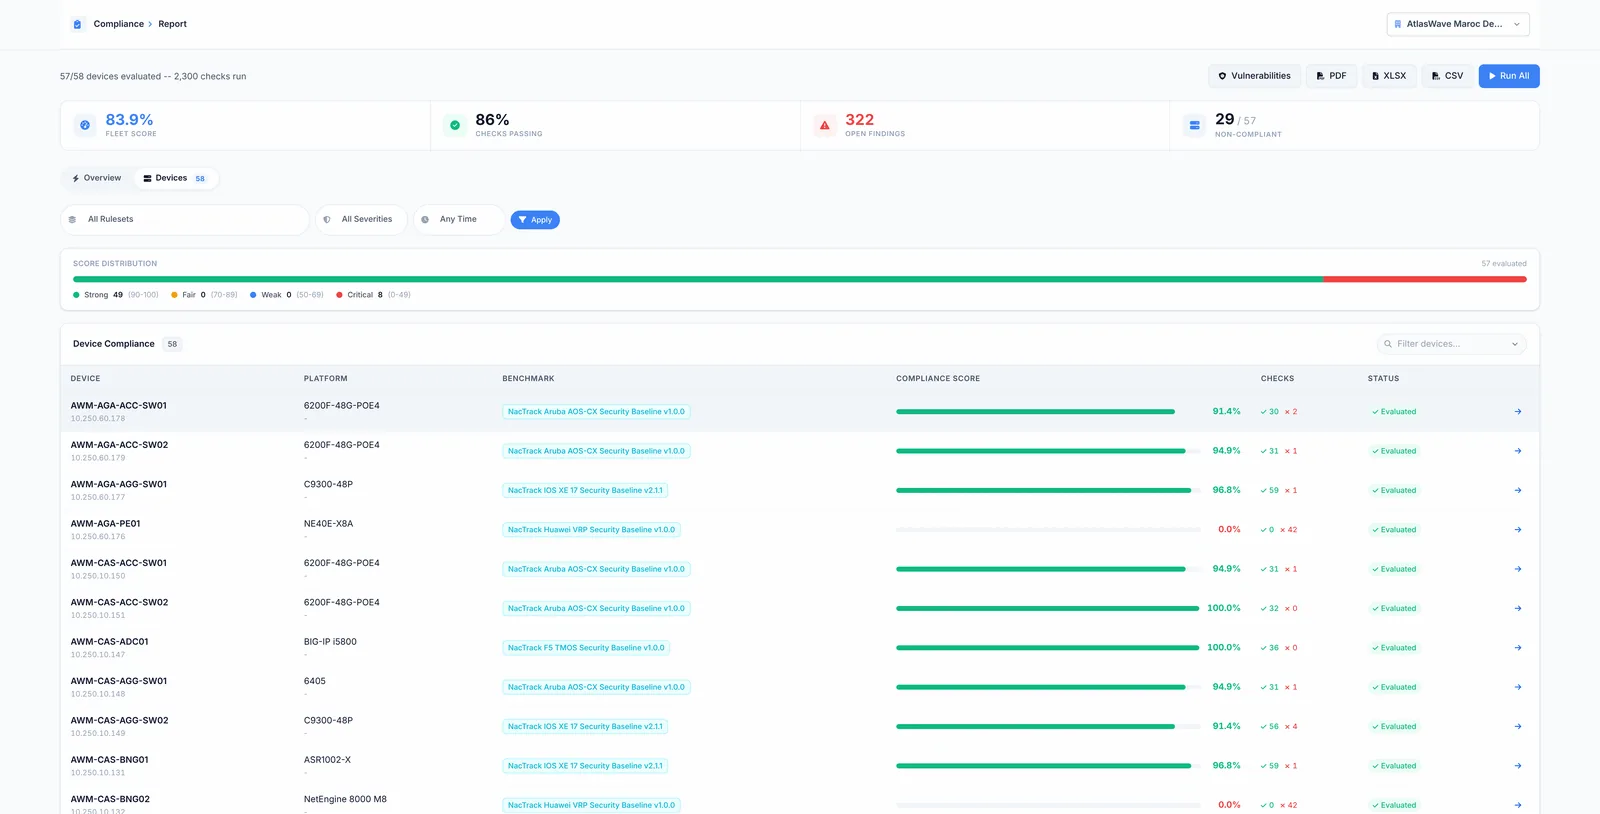
A number without evidence does not hold in a meeting. Every compliance finding carries the rule applied and the configuration extract that triggers it.
That is the difference between a report that gets argued with and a report that gets acted on.
The two risks this addresses
Regulatory risk. An audit asks for a current inventory, a hardening state and exposure tracking. Produced by hand, it ties up a team for weeks and is stale a month later.
Continuity risk. A device past vendor support becomes unrepairable without warning, and that is discovered on the day it fails.
Neither is an advanced security risk. Both are inventory risks.
- On your infrastructure, nothing leaves the building
- Your data never leaves the building
- No agent installed on the devices
- No change window needed
- Dated, exportable reports that belong to you
Look at it on a real estate before discussing it
The demo takes a minute to request and the account arrives by email, read only. The one day audit produces a report that belongs to you, whether or not anything follows.