Security
How to check whether a device still allows Telnet
Telnet carries passwords in clear text. Most networks turned it off years ago, which is exactly why the ones still answering on port 23 are easy to miss: they are usually not the devices anyone is worried about. NacTrack evaluates the collected configuration against a hardening benchmark for the platform, so the answer comes from what the device is actually running rather than from what the standard build was supposed to contain.
Before you start
What you need
- Module required: compliance.
- Permission required: view_audit.
- All benchmarked platforms; every shipped ruleset carries a Telnet check
1. Read the fleet scores
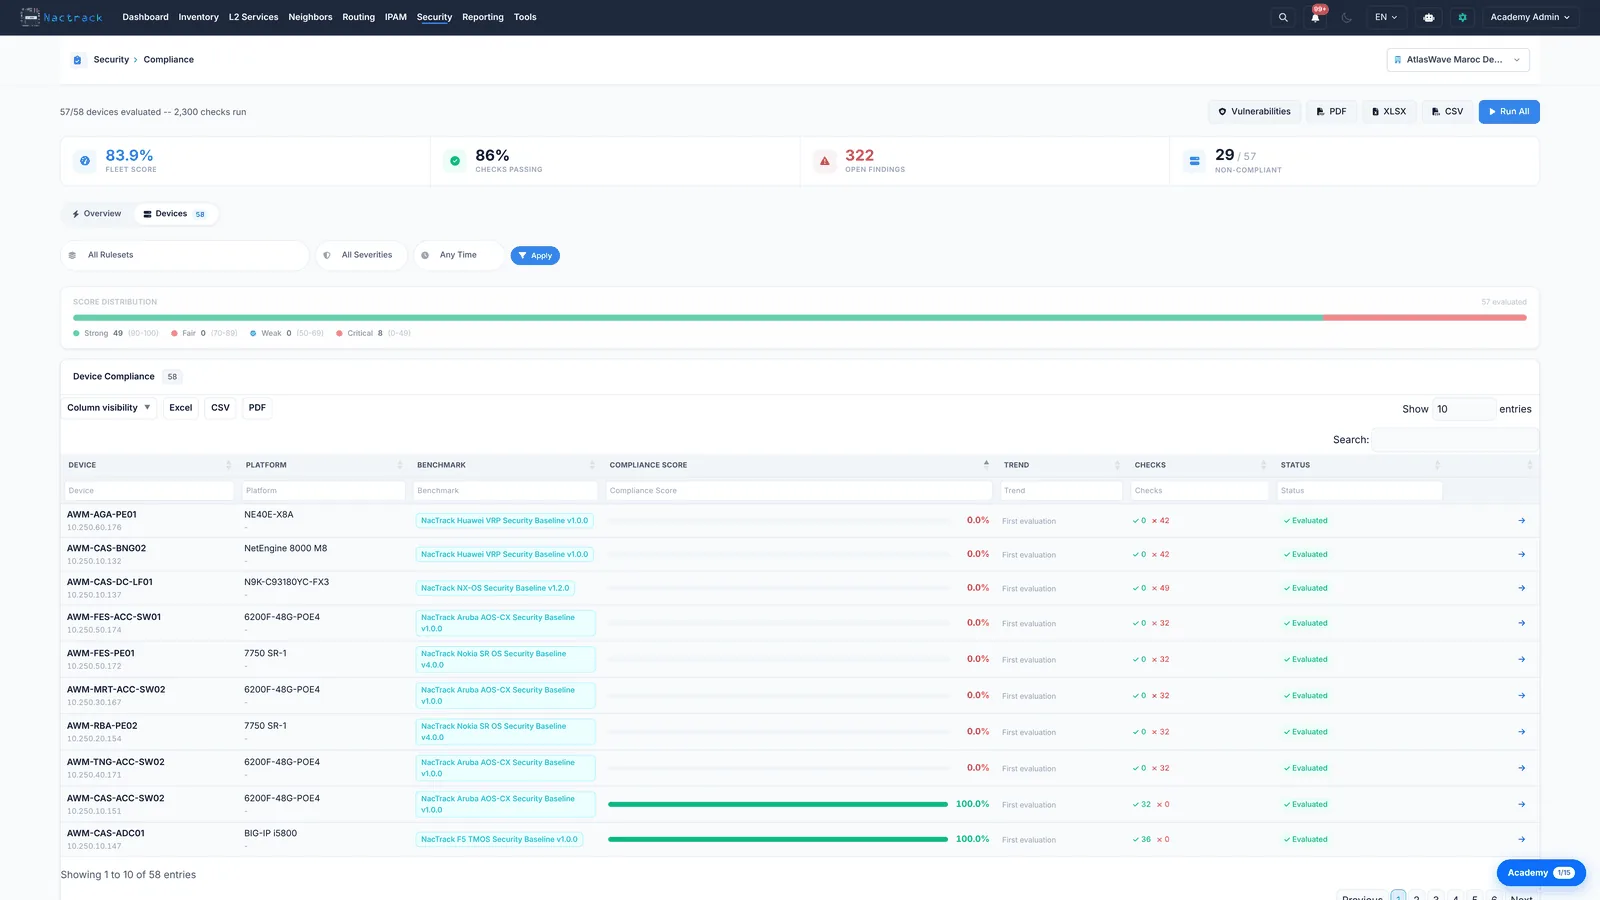
2. Open one device
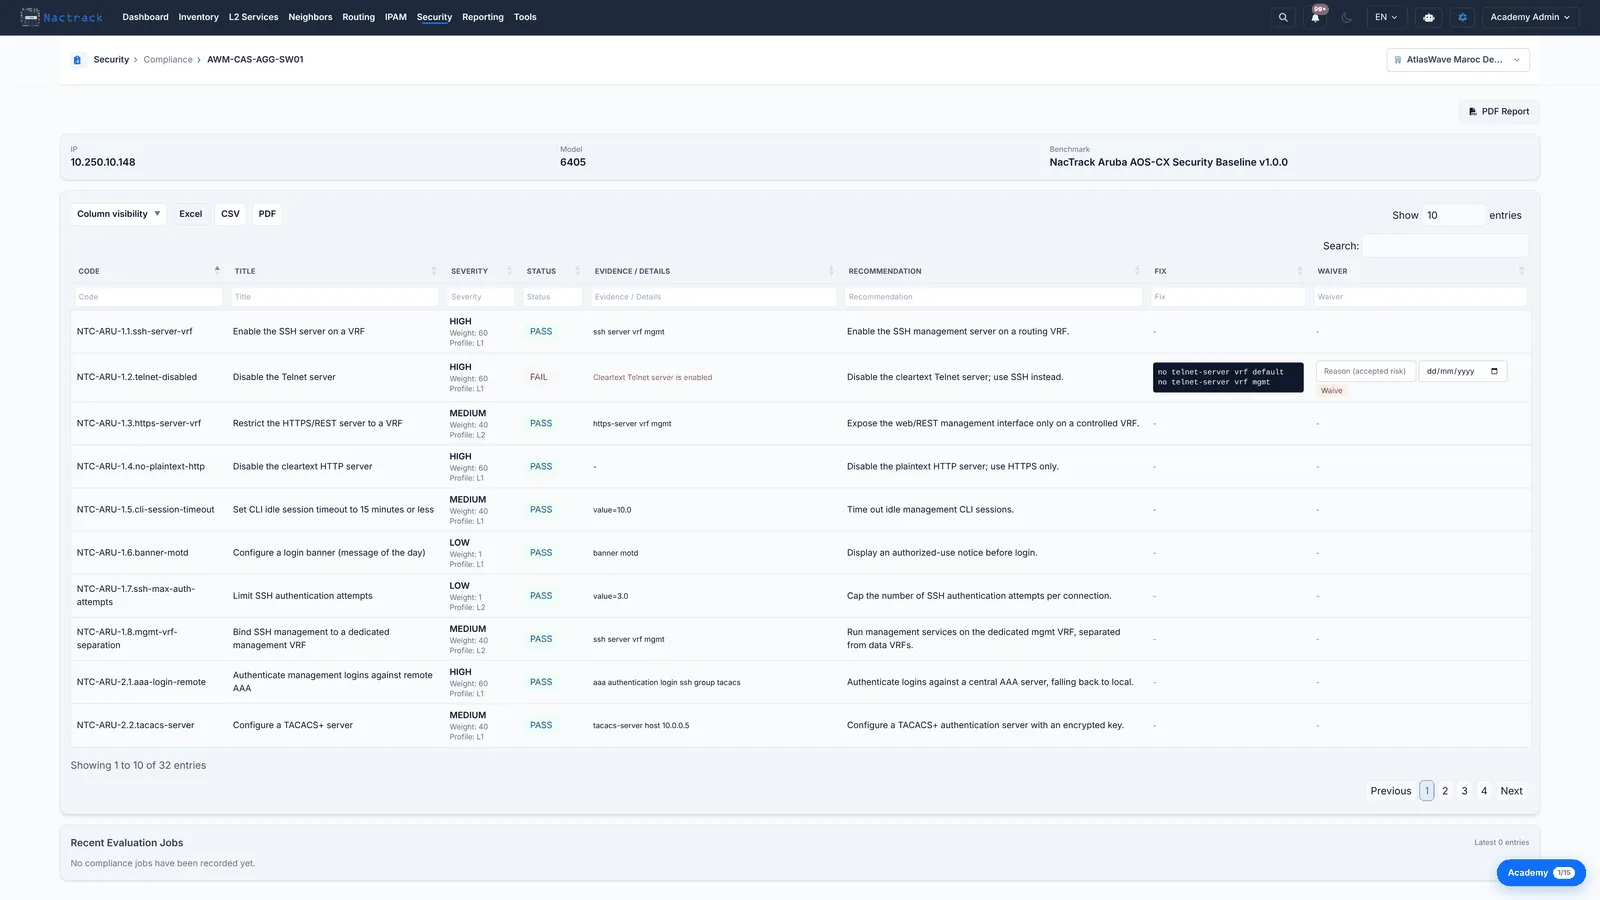
3. Read the finding
The limits
What this view does not tell you
- This reads configuration, not reachability. A device whose Telnet server is enabled may still be unreachable on port 23 because a firewall or a management ACL blocks it. The finding says the door is unlocked, not that anyone can walk to it.
- The verdict is only as fresh as the last configuration collection. A device hardened this morning still reads as failing until it is collected and evaluated again.